Most SaaS teams track churn through usage, support tickets and renewal dates. These matter, but they miss a quieter reason customers leave: they stop trusting you with their data.
A buyer rarely writes “privacy concerns” in a cancellation survey. More often the account goes quiet after a security questionnaire goes unanswered, an admin notices odd logins, or a compliance review raises doubts. By the time it shows up as churn, the decision was made weeks earlier.
This guide explains how trust, data privacy and identity verification affect B2B retention, and how to turn them into signals your customer success team can act on.
Why trust is a retention metric
In B2B, your product often touches sensitive things: customer records, financial data, employee information or internal documents. Your buyer is not only choosing features. They are also choosing a vendor they can defend to their own security team, legal team and board.
That changes how churn works:
- A security incident can end a renewal on its own, even if usage was strong.
- Compliance reviews can block expansion. A customer who loves the product may still not grow it if you cannot pass their review.
- Champions leave, and trust has to survive without them. A new decision-maker will ask harder questions than the person who bought you.
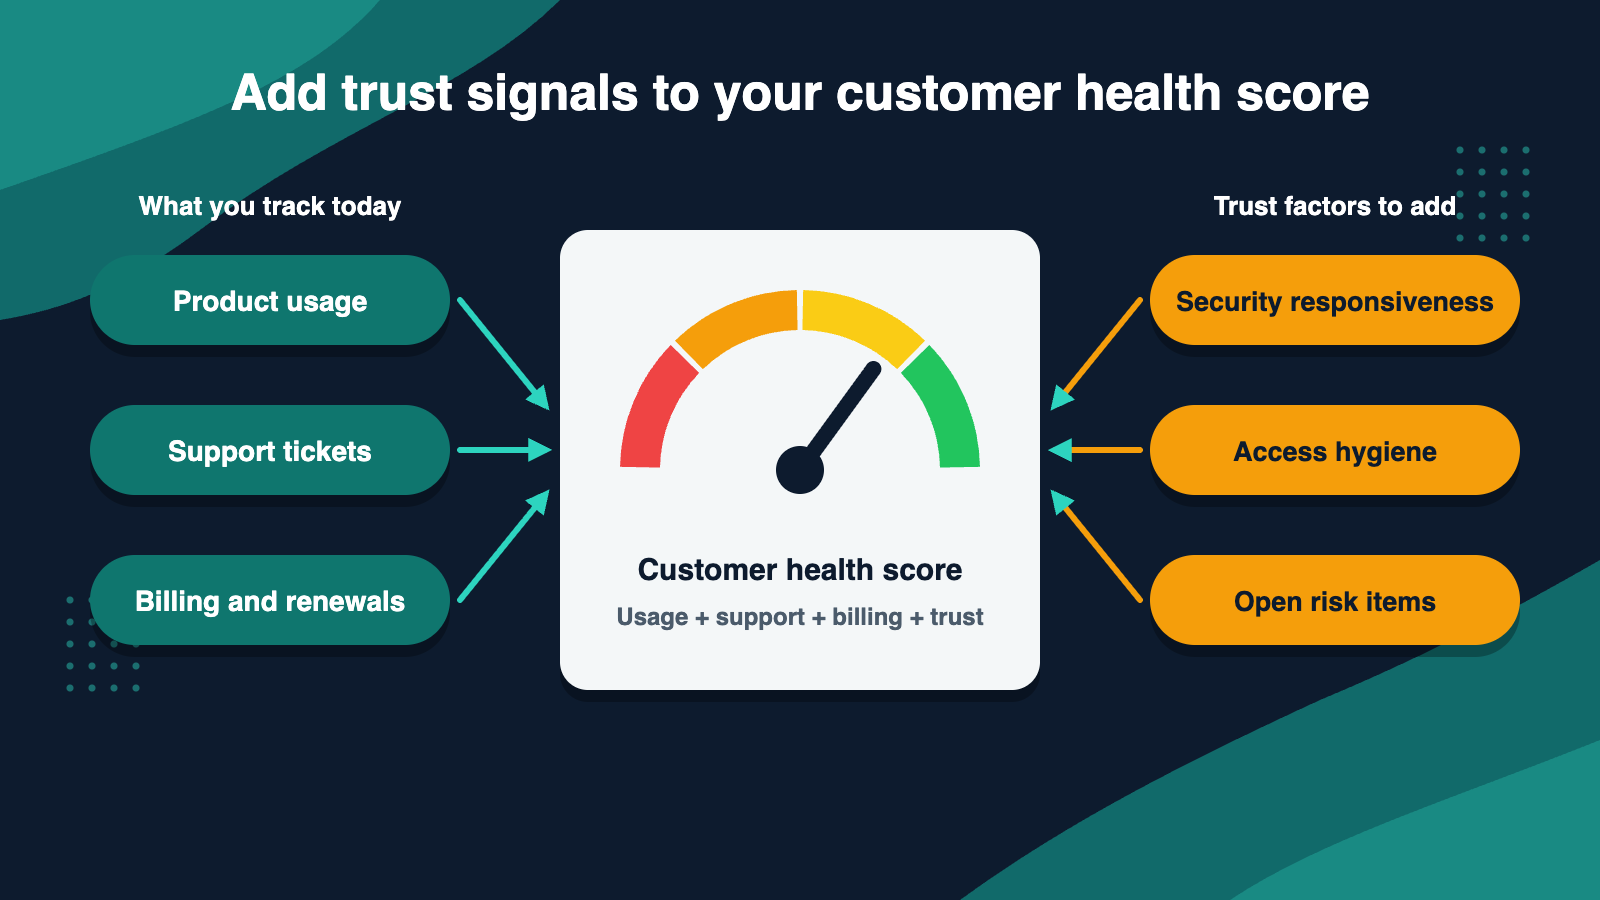
This is why trust belongs next to usage and engagement in your customer health score. A highly active account with unresolved security concerns is not healthy.
Data privacy: the expectations buyers now bring
Data privacy is no longer a legal footnote. Buyers ask where data is stored, who can access it, how long you keep it and how you respond to a breach. A solid grounding in online privacy and data protection helps your team answer these questions with confidence instead of scrambling.
Three habits protect retention here:
- Answer security questions fast and consistently. Keep a current security overview, data processing terms and a list of sub-processors ready. Slow or vague answers read as risk.
- Be clear about data handling. Explain what you collect and why. Surprises, such as a new data use buried in updated terms, damage trust quickly.
- Communicate before customers have to ask. Tell customers about security improvements, certifications and policy changes before renewal, not during the cancellation conversation.
Good information security practice also makes this easier. Teams that treat it as part of how they run the business, rather than a one-off audit, spend far less time reacting.
Identity verification: who is actually using your product?
Privacy covers how you handle data. Identity verification covers a related question: are the people accessing the account who they say they are?
For B2B SaaS this matters in several places:
- Onboarding. Verifying who is signing up helps you avoid fake or fraudulent accounts from the first day. A KYC verification step is standard in regulated sectors such as finance and crypto, and many other teams now use lighter versions.
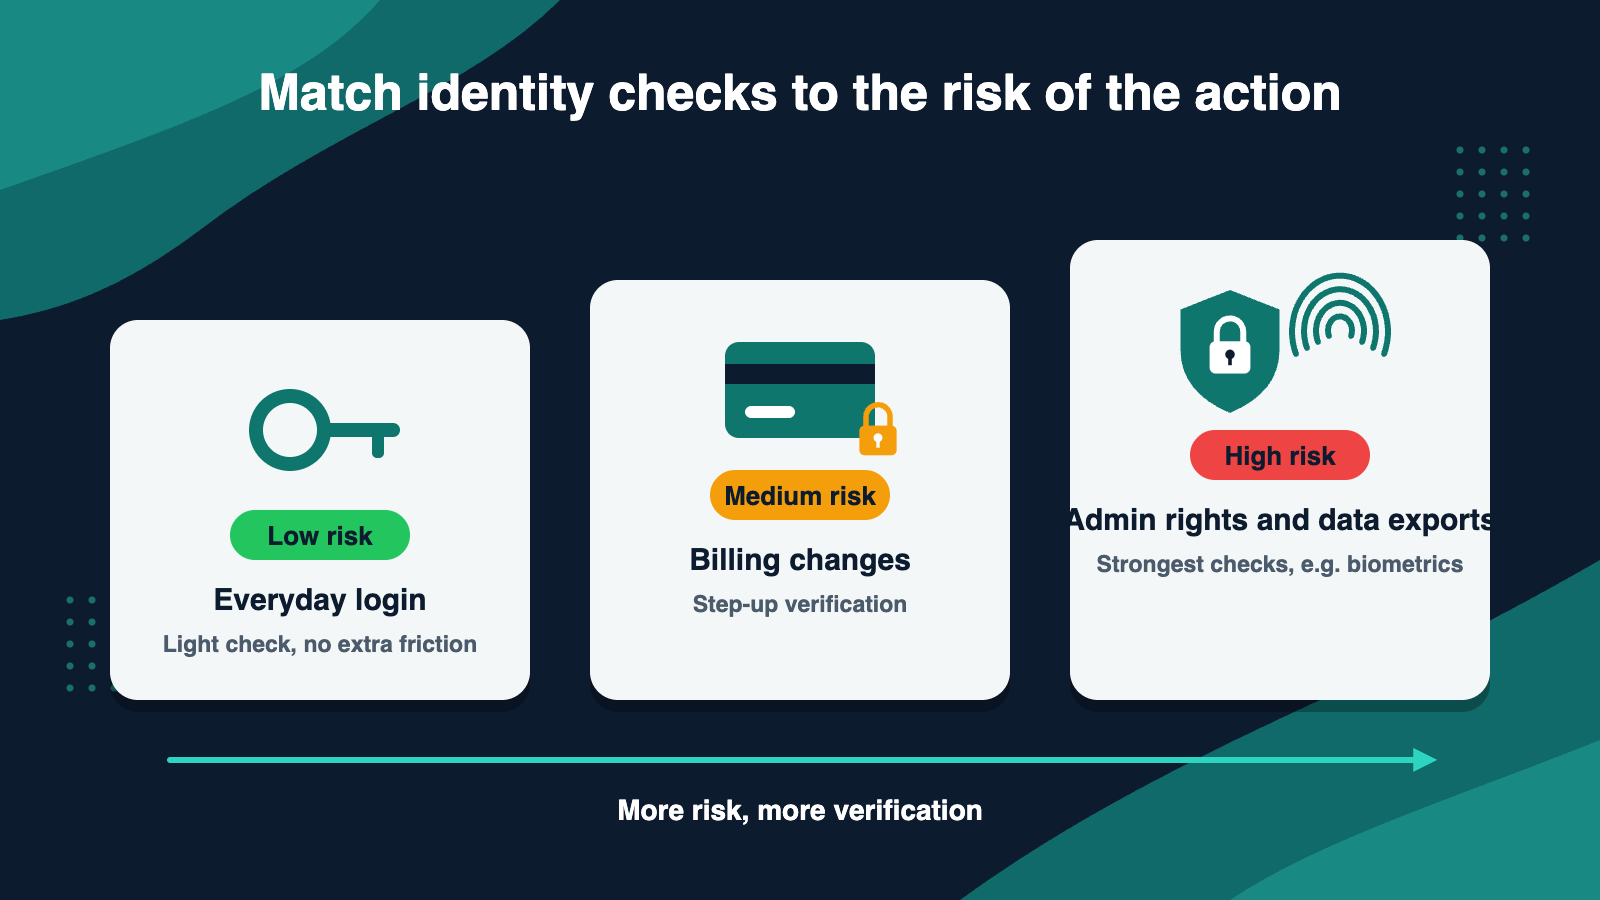
- Access control. Admin rights, billing changes and data exports should require stronger checks than a normal login. Methods such as biometric authentication are one option for higher-risk actions.
- Fraud and fake accounts. Fake signups, shared credentials and account takeovers all distort your numbers and hurt real customers. Strong fraud prevention keeps your data cleaner and your customers safer.
A note on balance: identity checks add friction. Done badly, they cause the very churn you want to avoid. Done well, they stay invisible for low-risk actions and appear only when the stakes justify them.
How trust gaps show up as churn signals
You can turn these ideas into things your team can watch. Here are warning signs worth adding to your churn tracking:
| Signal | What it may mean |
|---|---|
| Security questionnaire unanswered or delayed | Procurement or legal is hesitating |
| Admin contacts you about login or access issues | Concern about account safety |
| Sudden drop in logins from several named users | Champion left, or team lost confidence |
| Request for compliance documents near renewal | Formal review in progress |
| Unusual login patterns or shared accounts | Possible account-sharing or security risk |
| Seats added by unknown users | Governance gap on the customer side |
None of these proves a customer will leave. Together with usage data, they give your team an early warning, which is the whole point of retention work.
Add trust to your health score
A simple way to start is to add one or two trust factors to your scoring model:
- Security and compliance responsiveness: Were questions answered on time?
- Access hygiene: Are inactive users removed? Are admin roles reviewed?
- Open risk items: Any unresolved security tickets or pending reviews?
Give these a modest weight at first and check whether they predict churn in your own data. If they do, increase their influence. If not, simplify. As with any scoring model, your results should guide you, not assumptions.
If you use machine learning to predict churn, trust and security factors can be useful features alongside usage and billing data. Machine learning works best when it is fed signals that reflect real customer behaviour, which includes how customers respond to security and compliance events.
A simple playbook for trust-related risk
When a trust signal appears, treat it like any other at-risk account:
- Flag it early. Create an alert when a signal such as an overdue security review shows up.
- Assign an owner. Customer success should work with security or legal, not alone.
- Respond quickly and plainly. Give clear answers, supporting documents and a named contact.
- Follow up. Confirm the customer is satisfied before the renewal conversation.
- Record what you learned. Update your save playbook so the next case is faster.
Common mistakes to avoid
- Treating security as only an engineering job. Customer success and revenue teams see the trust signals first.
- Waiting for the renewal call. By then, concerns have usually hardened.
- Adding heavy identity checks everywhere. Friction without a reason frustrates good customers.
- Ignoring cloud and infrastructure expectations. Buyers increasingly ask about cloud security and compliance, so have clear answers ready.
- Measuring only usage. An active account can still be at risk.
Quick checklist
- Keep security documents current and easy to share
- Define who answers security questionnaires and how fast
- Verify identity at signup and for high-risk actions
- Add one or two trust signals to your health score
- Flag security-related delays as churn risk
- Review access and admin roles with key accounts before renewal
- Update your save playbook with trust-related steps
Final thoughts
Features win deals, but trust keeps them. Customers stay longest with vendors who protect their data, know who is using the product and communicate clearly when something changes.
You do not need a large security team to start. Add a few trust signals to what you already track, respond fast to security questions, and verify identity where it matters. These steps make your customers safer, and they make your retention numbers more reliable too.